Read a Trust Check Result
Specifications:
- IETF RFC 5280 §6 (the path checks)
- ETSI TS 119 612 V2.4.1 §5.5 and ETSI TS 119 602 V1.1.1 §6.6 (the service, its status and its digital identity in the matched entry)
In short
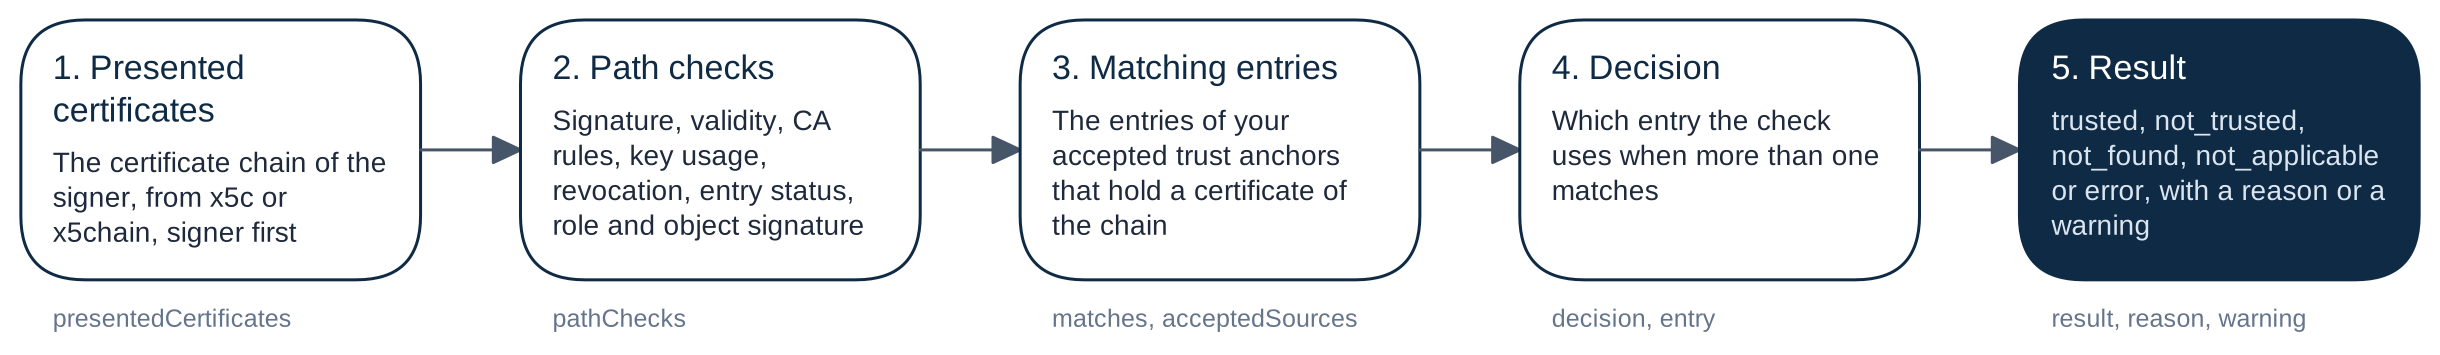
- Every trust check of the iGrant.io Organisation Wallet Suite records its result in the same shape, a trusted list check, wherever it runs: issuance, verification or the organisation wallet.
- It says whether the signer is trusted, for which role, which entry of which trust anchor matched, and why not when it is not.
- It also keeps the certificates that the signer presented and the result of each check on the path, so that you can see exactly what was checked.
The shape of a check
{
  "verified": true,
  "result": "trusted",
  "role": "pid_provider",
  "entry": {
    "entryId": "fYzBWmw8vWBPbY_y5R-Ilg",
    "status": "granted",
    "roles": ["pid_provider"],
    "provider": { "tSPName": "Example PID Provider" },
    "service": { "serviceTypeIdentifier": "http://uri.etsi.org/19602/SvcType/PID/Issuance" },
    "source": {
      "id": "71c85eab-312e-461c-82f9-dbcd61b0bece",
      "name": "NXD Trust List: PID providers",
      "kind": "etsi_lote"
    }
  },
  "reason": null,
  "warning": null,
  "presentedCertificates": [
    { "subject": "CN=Example PID Signer", "issuer": "CN=Example PID CA", "certificate": "MIIC..." }
  ],
  "pathChecks": [
    { "code": "signature", "result": "passed" },
    { "code": "validity", "result": "passed" },
    { "code": "caRules", "result": "passed" },
    { "code": "keyUsage", "result": "passed" },
    { "code": "revocation", "result": "not_checked" },
    { "code": "entryStatus", "result": "passed" },
    { "code": "role", "result": "passed" },
    { "code": "objectSignature", "result": "passed" }
  ]
}
| Member | Content |
|---|---|
verified | true only when result is trusted |
result | trusted, not_trusted, not_found (in no accepted trust anchor), not_applicable (the Require switch is off) or error (the check could not decide) |
role | The role that the check asks for |
entry | The matched entry: its entryId, status, roles, provider, service and trust anchor (source) |
reason | Why the result is not_trusted, not_applicable or error |
warning | Why a trusted result has a warning |
presentedCertificates | The certificates that the signer presented, the signer certificate first (base64 DER) |
pathChecks | The result of each check on the path: passed, failed or not_checked. See Certificates and Chains. |
matches | Every entry that matched the chain, with its result and its trust anchor. The check uses one of them. |
decision | Why the check used that entry, when more than one matched |
acceptedSources | The trust anchors of the accepted list of the setting |
Older records may have only some of these members.
Why a signer is not trusted
reason.code | Meaning |
|---|---|
not_required | The Require switch of the check is off, so no check ran |
same_as_credential_signer | The credential signer signed the status list, and the setting accepts it (a trusted result with no list lookup) |
not_accepted | The client ID of the request is not one of the accepted client IDs |
wrong_role | The entry is listed for another role |
not_granted | The status of the entry is not granted, for example withdrawn |
certificate_not_valid | The certificate of the entry is not valid now |
path_not_valid | A signature of the certificate path does not verify |
ca_rules_not_met | A CA of the path may not issue certificates |
key_usage_not_allowed | The signer certificate may not make signatures |
revoked | The signer certificate is revoked |
object_signature | The object is not signed with the key of the signer certificate |
ski_only | The entry gives only a key identifier, which cannot verify a signature |
list_not_downloaded | An accepted list is not downloaded, and nothing else matched (error) |
check_failed | The check could not run, with a message (error) |
Warnings
A trusted result can carry a warning. The signer passes, but you should look:
warning.code | Meaning |
|---|---|
entry_status | The entry has an unusual status, or a TS 119 612 entry has no status |
list_expired | The match is in an expired list, from its last stored copy |
entity_ambiguous | Entries of more than one organisation list the signer, and its certificate names none of them |
status_conflict | The entries that list the signer do not agree on its status. The check used the valid entry. |
Where checks are recorded
| Where | Member |
|---|---|
| Issuance history: the wallet instance attestation | authorisation.walletUnitAttestation.walletProviderTrustedListCheck |
| Issuance history: a key attestation | authorisation.keyAttestation.walletProviderTrustedListCheck, or platformRootCheck for an Android hardware Keystore key |
| Verification record: each presented credential | presentationValidity[].<credential query id>.credentialSignerTrustedListCheck and .statusIssuerTrustedListCheck (for a query with multiple, under credentials[]) |
| Organisation wallet: a held credential | credentialSignerTrustedListCheck, issuerTrustedListCheck and statusIssuerTrustedListCheck |
| Organisation wallet: a presentation | relyingPartyTrustedListCheck |
In the dashboard
Each check shows as a trust chip:
| Chip | When |
|---|---|
| Trusted (green) | The result is trusted |
| Trusted, with a warning (amber) | The result is trusted and has a warning |
| Not trusted (red) | The result is not_trusted or not_found |
| The check failed (orange) | The result is error |
| Not checked (grey) | No check ran, for example because the Require switch is off. The hover text names the switch. |
The chip of a party, at the top of a record, shows its worst row. Select a chip to open its trust panel. The title of the panel is Trust: with the name of the row, for example Trust: Wallet provider, or Trust in the signer. The panel has these cards:
- Result: the result and why, the role that the check asked for (Checked for the role) and the Accepted trust anchors.
- Certificate chain: the certificates that the signer sent, signer first. When your trust anchor lists the CA above them, that CA comes last, under From your trust anchor and its name. Show technical details has the copy and the download of each certificate.
- Checks: the result of each check on the path.
- Entries that match: the entry that the check used (Used), and the other entries with Valid, Valid, with a warning or Not valid.
Select an entry to open it in its trust anchor.